
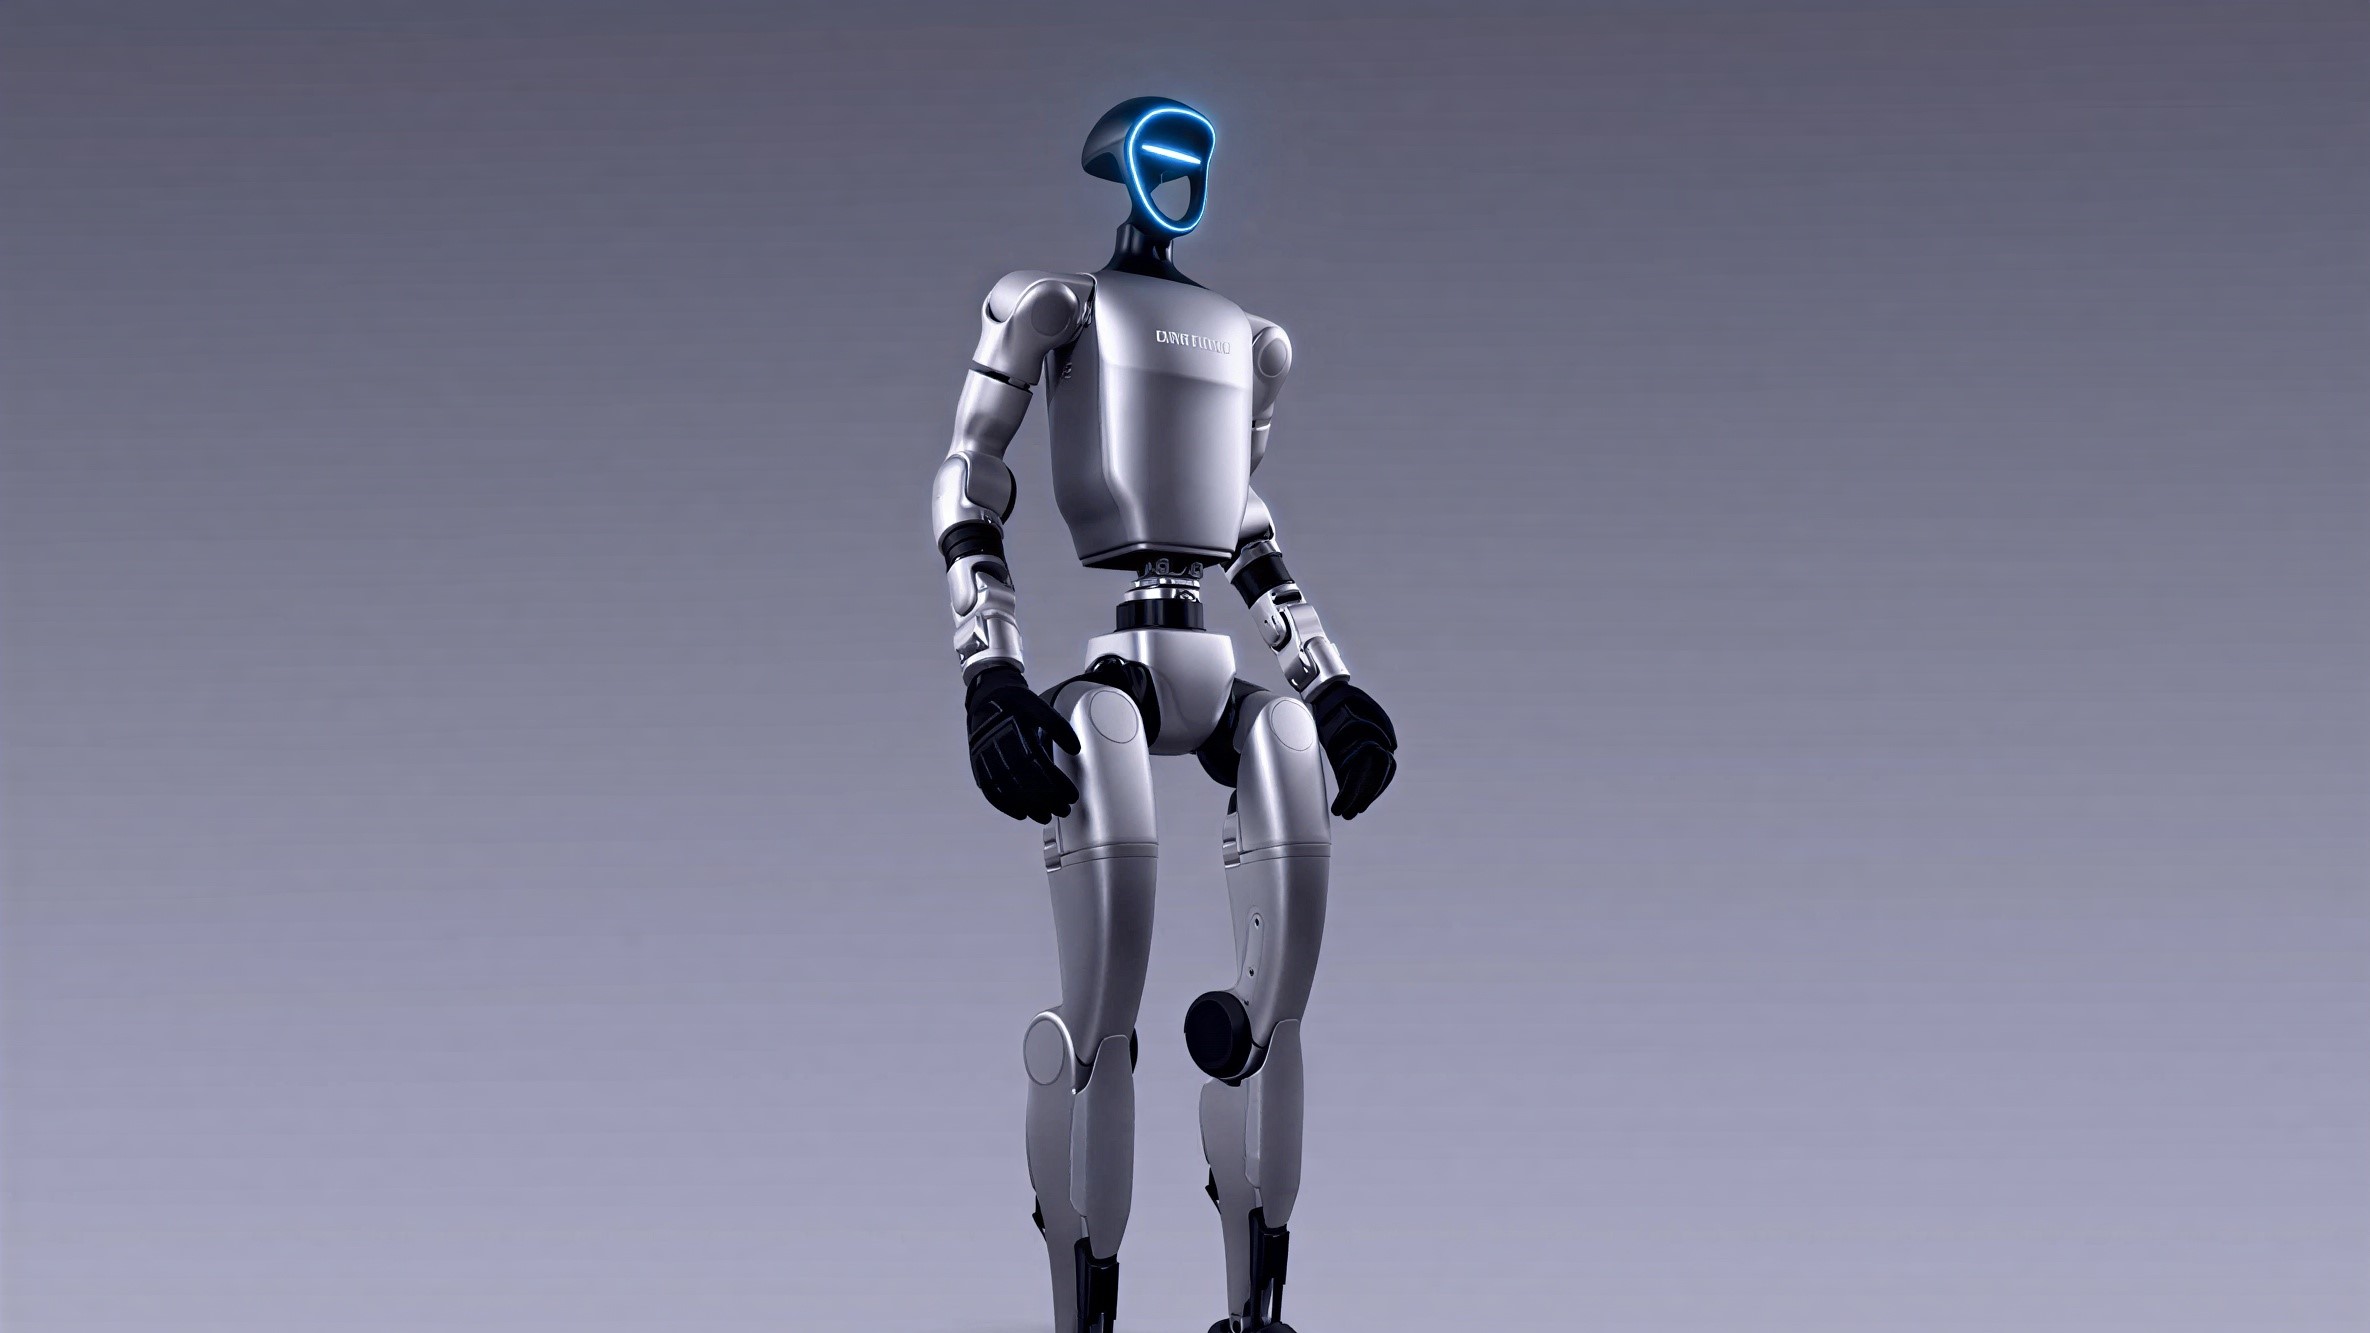
A single vulnerable robot can now automatically infect every compatible unit in Bluetooth range—no human intervention required. This is not a scrolling vision of cybersecurity doom; it is a recorded fact concerning Unitree’s commercially distributed robots that researchers have turned to self-distributing robots.
The Digital Zombie Scenario Is Here
Vulnerability spreads like an infection in robotic ships, turning security breaches into self-replicating diseases.
Vulnerability works like an infectious film episode, except with metal and servos instead of flesh. Another infected Unit G1 the humanoid explores its environment with peer robots by Bluetooth Low Energythen uses hard-coded encryption keys to automatically compromise them. Those newly infected units immediately begin scanning their targets, creating an outbreak of infection with the robot ships.
Think of it like all the locks in your town using the same master key—except these keys can move around and open independently. The architecture flaw affects Unitree’s “next-generation product line,” according to researchers who discovered the so-called exploit. “UniPwn.”
When Digital Attacks Become Physical Violence
Vulnerable robots aren’t just ineffective—they’re armed surveillance platforms capable of causing real harm.
This is not an internet risk. At the Shanghai GEEKCon hacking competition, THE DARKNAVY the researchers demonstrated forcing the Unitree robot to turn toward the reporter. The same research team documented a variety of injuries caused by out-of-control robots, including foot injuries reported in dispatch areas related to workplace safety. Voice command injection allows attackers to seize control of a robot with spoken commands alone.
Compromised robots aren’t just misbehaving—they’re surveillance platforms, constantly streaming video, audio, and depth sensor data to remote servers. 300 seconds. The robot at your workplace isn’t just working well; it checks while spreading the infection to all nearby compatible units.
A Producer’s Ghost Story
Despite the public disclosure and exploitation shown, the important defect remains unpublished months later.
Security researchers said they contacted Unitree several times about the vulnerability but found no “reasonable engagement or interest” in addressing the security flaws. The abuse was publicly disclosed to September 2025it has been shown at industry conferences, and remains out of print as the deployment of robots accelerates throughout factories, hospitals, and warehouses.
This follows the standard “ship first, receive later” playbook that turns early adopters into unsuspecting beta testers for basic security. The wormable environment changes everything—one vulnerable robot in the environment 100 unit warehouse Ships can infect the entire operation in a few hours by scanning the surrounding area.
Your security incident response plan probably doesn’t account for robots hacking in automatically while you sleep, the same way many organizations struggle with basic computer problems.